
2026 US Data Security Law Recap
From the Ashurst Perkins Coie law firm: Read more about specific state updates at JDSupra.


New research from Netskope Threat Labs has found that 83% of AI-related security alerts in manufacturing involve employees sharing information with AI tools in ways that breach company policies. As CXOToday reports: This makes it the most prevalent AI-related security risk facing manufacturers, with employees potentially exposing confidential documents or sensitive company data through their use of AI applications. Downstream data policy violations, where AI systems return information to users that are not supposed to see it, are making up

A press release from the Cybersecurity and Infrastructure Security Agency (CISA): Today, the Cybersecurity and Infrastructure Security Agency (CISA) unveiled the updated cyber incident reporting form, an enhanced web-enabled questionnaire available on CISA’s Incident Reporting Portal for reporting cyber incidents. By improving data quality, the more robust form strengthens the effectiveness and efficiency of national cyber defense. For instance, the new form will help CISA correlate related cyber threat activity to identify a larger trend from what otherwise would appear
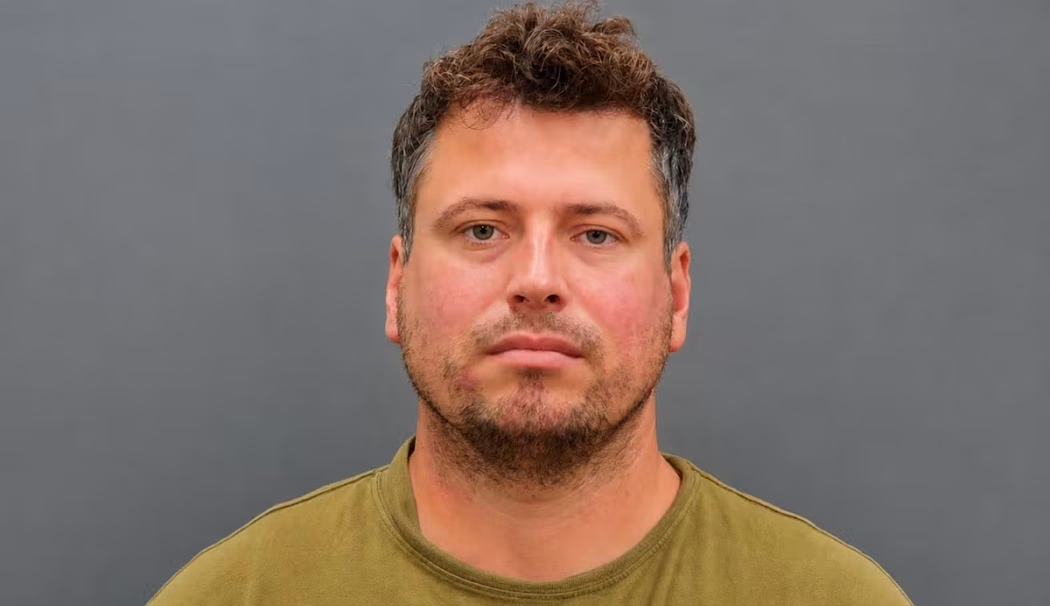
The Record reports: A senior FBI official pleaded guilty to stealing millions in cryptocurrency from wallets controlled by nation-state hackers and theft victims. Patrick Steven Yaroch, 37, is facing up to 20 years in prison on wire fraud and money laundering charges after admitting to using his position on an FBI investigative squad to steal more than $2.4 million in cryptocurrency to cover his debts. Yaroch was an FBI Supervisory Special Agent who worked at FBI Headquarters within the Counterintelligence
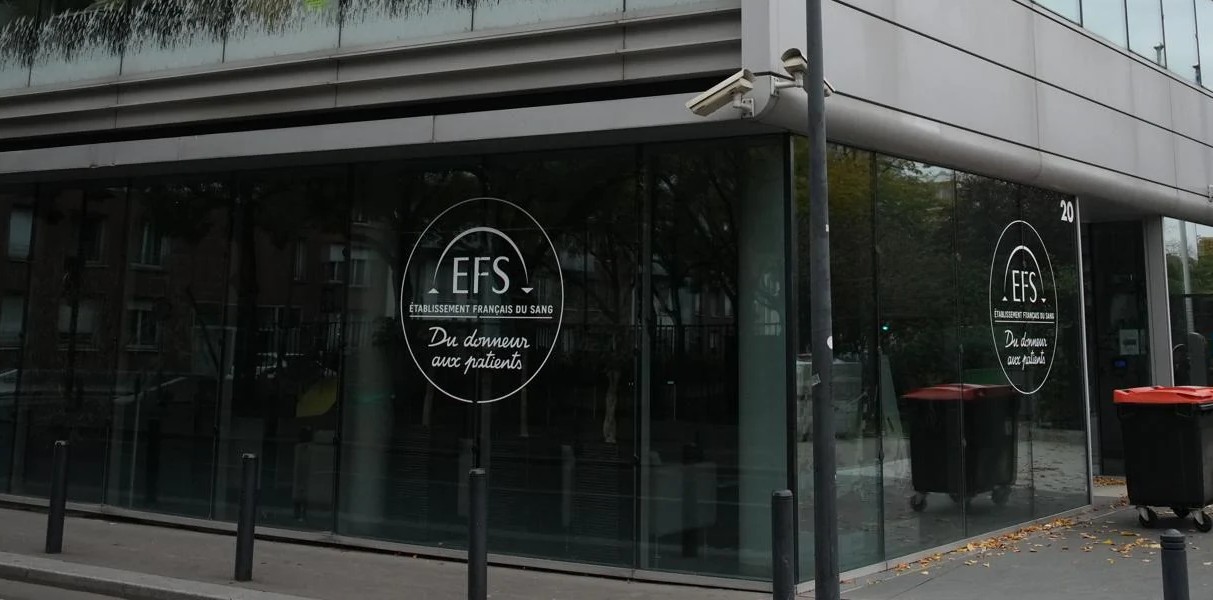
Digital Shield reports: France has once again been targeted by cybercriminals. This time, the cyber attackers have focused on the French Blood Service (Établissement Français du Sang or EFS) in an incident whose modus operandi is very reminiscent of the recent hacking of some French supermarket chains. The threat actors intervened in the temperature control systems of the equipment of the refrigeration service provider Coolworld. The EFS uses this company’s refrigerators to store therapeutic plasma and blood samples intended for
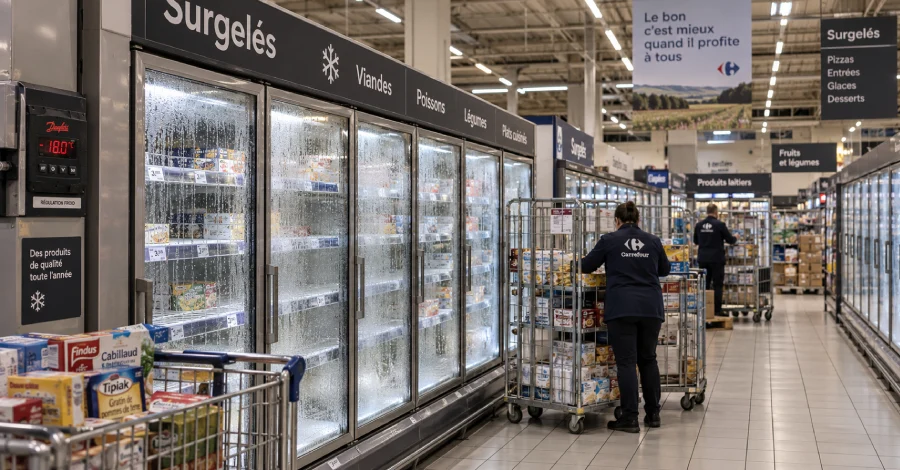
Round 2? ABC News (AU) reports: Multiple supermarket and grocery chains across Europe have reported an IT incident affecting fridges and freezers overnight, with one company attributing the temperature spikes to a cyber attack. Dutch supermarket chain Ahold Delhaize and Belgian chain Colruyt said on Monday a tech incident overnight hit cold storage in dozens of stores in Belgium and Luxembourg, while Swedish grocers ICA and Coop reported similar temperature spikes. Swedish retailer Ikea also reported that one of its
New research from Netskope Threat Labs has found that 83% of AI-related security alerts in manufacturing involve employees sharing information with AI tools in ways that breach company policies. As CXOToday reports: This makes it the most prevalent AI-related security risk facing manufacturers, with employees potentially exposing confidential documents or sensitive company data through their use of AI applications. Downstream data policy violations, where AI systems return information to users that are not supposed to see it, are making up
A press release from the Cybersecurity and Infrastructure Security Agency (CISA): Today, the Cybersecurity and Infrastructure Security Agency (CISA) unveiled the updated cyber incident reporting form, an enhanced web-enabled questionnaire available on CISA’s Incident Reporting Portal for reporting cyber incidents. By improving data quality, the more robust form strengthens the effectiveness and efficiency of national cyber defense. For instance, the new form will help CISA correlate related cyber threat activity to identify a larger trend from what otherwise would appear
The Record reports: A senior FBI official pleaded guilty to stealing millions in cryptocurrency from wallets controlled by nation-state hackers and theft victims. Patrick Steven Yaroch, 37, is facing up to 20 years in prison on wire fraud and money laundering charges after admitting to using his position on an FBI investigative squad to steal more than $2.4 million in cryptocurrency to cover his debts. Yaroch was an FBI Supervisory Special Agent who worked at FBI Headquarters within the Counterintelligence
Digital Shield reports: France has once again been targeted by cybercriminals. This time, the cyber attackers have focused on the French Blood Service (Établissement Français du Sang or EFS) in an incident whose modus operandi is very reminiscent of the recent hacking of some French supermarket chains. The threat actors intervened in the temperature control systems of the equipment of the refrigeration service provider Coolworld. The EFS uses this company’s refrigerators to store therapeutic plasma and blood samples intended for